Security teams are exhausted, and honestly, who could blame them? Modern software moves fast, threats evolve faster, and vulnerabilities rarely wait politely in line to be discovered, prioritized, and fixed. They pile up. They hide in dependencies, APIs, misconfigurations, and forgotten code branches. That is exactly why understanding an AI vulnerability scanner has become so important for vulnerability lifecycle management.
This is not just about catching flaws. It is about building a smarter, calmer, more resilient process from discovery to remediation to verification. When you look closely, AI-driven analysis is changing the rhythm of security work. It helps you see what matters first, what can wait, and where your teams may be wasting precious energy.
Why an AI vulnerability scanner matters in the real world
Traditional vulnerability management often feels like standing in a storm with a clipboard. Alerts pour in, scanners produce long lists, and teams must manually sort critical issues from background noise. An AI vulnerability scanner helps reduce that chaos by adding context, pattern recognition, and prioritization to raw findings.
Instead of simply reporting that a flaw exists, these tools can examine exploitability, environmental exposure, asset value, patch history, and code behavior. That means you are not just staring at a mountain of issues. You are getting a guided path through it.
There is something deeply human about that kind of help. Many teams do not fail because they lack talent. They struggle because they are overwhelmed. A good system does not replace judgment. It supports it.
See also: Mastering Index Technical Analysis for Consistent Profits in India
Understanding vulnerability lifecycle management
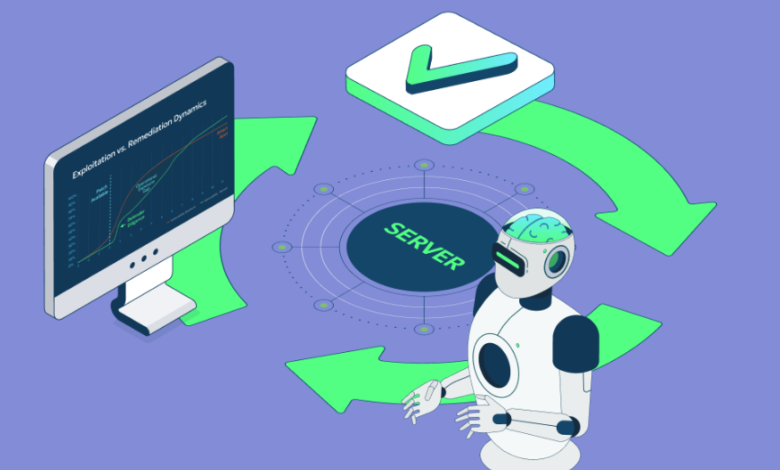
Vulnerability lifecycle management covers the full journey of a security weakness. First, a vulnerability is identified. Then it is validated, assessed, prioritized, assigned, remediated, and retested. Finally, the organization documents the outcome and folds those lessons back into future prevention.
That sounds neat on paper. In reality, every stage can break down.
Discovery tools may generate false positives. Security analysts may spend hours reviewing findings that are not urgent. Developers may receive tickets with little context. Leaders may not know whether risk is shrinking or silently expanding.
This is where AI becomes valuable. It can connect fragmented signals across systems and translate technical findings into more practical actions. In many organizations, that shift is the difference between reactive firefighting and a disciplined security program.
How AI code vulnerability scanner insights strengthen remediation
When vulnerabilities are rooted in software itself, teams need more than a generic alert. They need clarity about where the flaw lives, how dangerous it is, and which fix is most likely to work. An advanced, AI code security scanner can help analyze source code patterns, insecure functions, logic flaws, and dangerous dependencies with greater precision and context than basic static checks alone.
More importantly, it can support remediation guidance. That means developers are not left squinting at a cryptic warning and wondering what to do next. Instead, they can receive prioritized recommendations aligned with the actual structure of the application.
There is a small story worth sharing here about the word improve. A team lead once told a junior developer, “Do not chase perfection this sprint, just improve one risky habit at a time.” That advice changed the mood of the whole room. Security got better not through panic, but through steady progress. That is exactly the mindset AI should support. It should help you improve consistently, not drown you in impossible expectations.
Key capabilities to look for in AI-driven scanning
Not every platform delivers the same value, and not every AI feature is meaningful. Some tools simply layer flashy language over old workflows. If you are evaluating solutions, focus on practical capabilities.
Look for contextual prioritization. A scanner should help determine which vulnerabilities are actually exploitable in your environment.
Look for noise reduction. False positives waste time and slowly drain trust from security programs.
Look for remediation intelligence. Recommendations should be specific, actionable, and understandable to both security teams and developers.
Look for integration. The best tools fit into CI/CD pipelines, ticketing systems, cloud environments, and asset inventories.
Look for learning and adaptation. Strong systems get better as they process more data about your codebase, infrastructure, and historical fixes.
There is also an emotional layer to this. People need tools they can trust. Once trust is broken, adoption drops quickly.
Using AI code vulnerability scanner data to prioritize what truly matters
An AI code vulnerability scanner is especially useful when organizations struggle with too many findings and too few hands. It can correlate code-level issues with business impact, runtime exposure, and exploit intelligence, helping teams act where risk is most real.
That kind of prioritization is not a luxury anymore. It is survival.
There is another brief anecdote that fits here: a manager once described a legacy system as practically forsworn by the company, neglected because every team assumed someone else owned it. Months later, a severe vulnerability was found there. The lesson stung. Risks do not disappear just because attention does. AI-assisted lifecycle management can help surface those forgotten corners before they become painful headlines.
Common challenges and what to watch out for
AI is powerful, but it is not magic. You still need governance, testing, and human oversight. Poor data quality can weaken results. Weak integrations can create blind spots. Overreliance on automation can also become dangerous if teams stop questioning outputs.
Another challenge is explainability. If a scanner labels one issue critical and another low-risk, your teams need to understand why. Black-box scoring may look impressive, but it can frustrate analysts and developers who need evidence before they act.
And then there is the subtle risk of being beguiled by polished dashboards. One security architect once admitted that a beautiful interface almost convinced the team a platform was mature. It was charming, sleek, and strangely comforting. But under the surface, the detection logic was shallow. That moment was a reminder: never let appearances beguile your decision-making. Real value lives in accuracy, context, and workflow support.
Building a stronger lifecycle with AI
To get the best results, treat AI as part of a broader security operating model. Define ownership clearly. Establish SLAs for remediation. Feed scanner findings into development workflows. Track recurring vulnerability patterns. Review whether fixes actually reduce exposure over time.
The goal is not just faster scanning. The goal is a healthier lifecycle.
When used well, an AI vulnerability scanner gives your teams breathing room. It helps security analysts focus. It helps developers respond with confidence. It helps leaders understand where risk stands today, not weeks too late.
Vulnerability management has always been a race against time, complexity, and human fatigue. AI does not remove that reality, but it can make the race feel less lonely and far more winnable. If you want stronger resilience, clearer prioritization, and smarter remediation, this is where the future is already taking shape.